See it on a fictional account
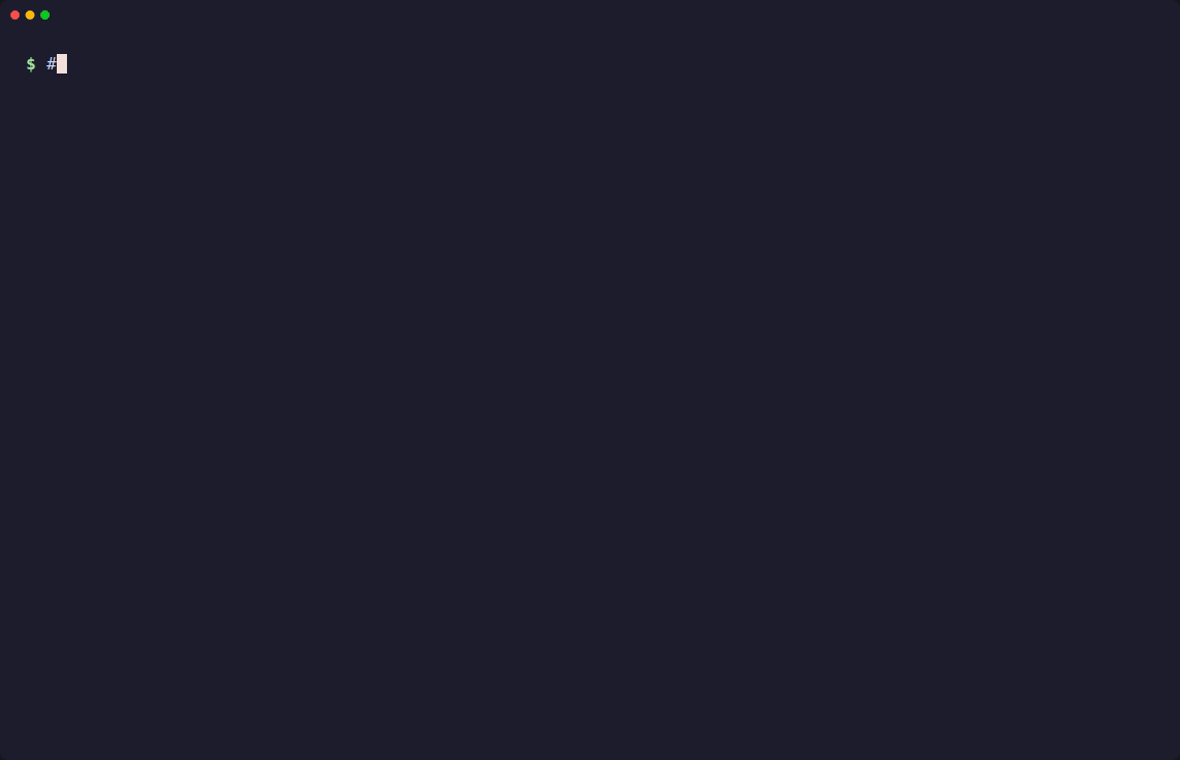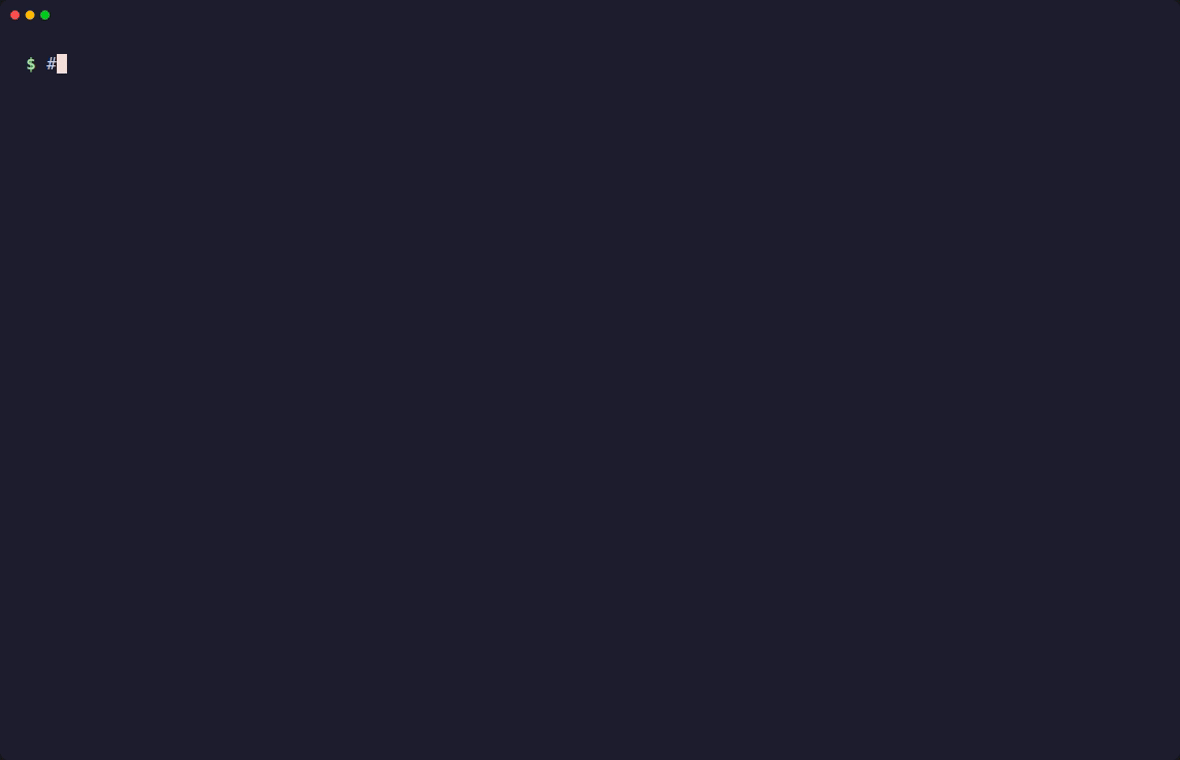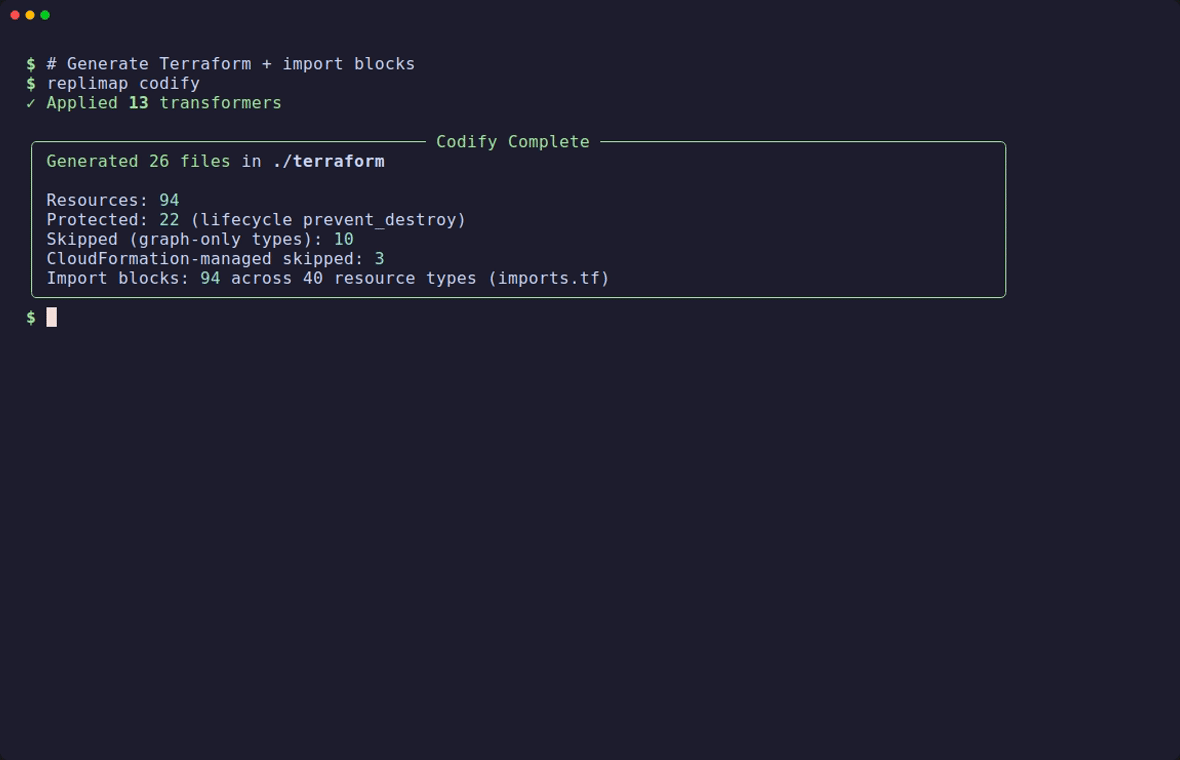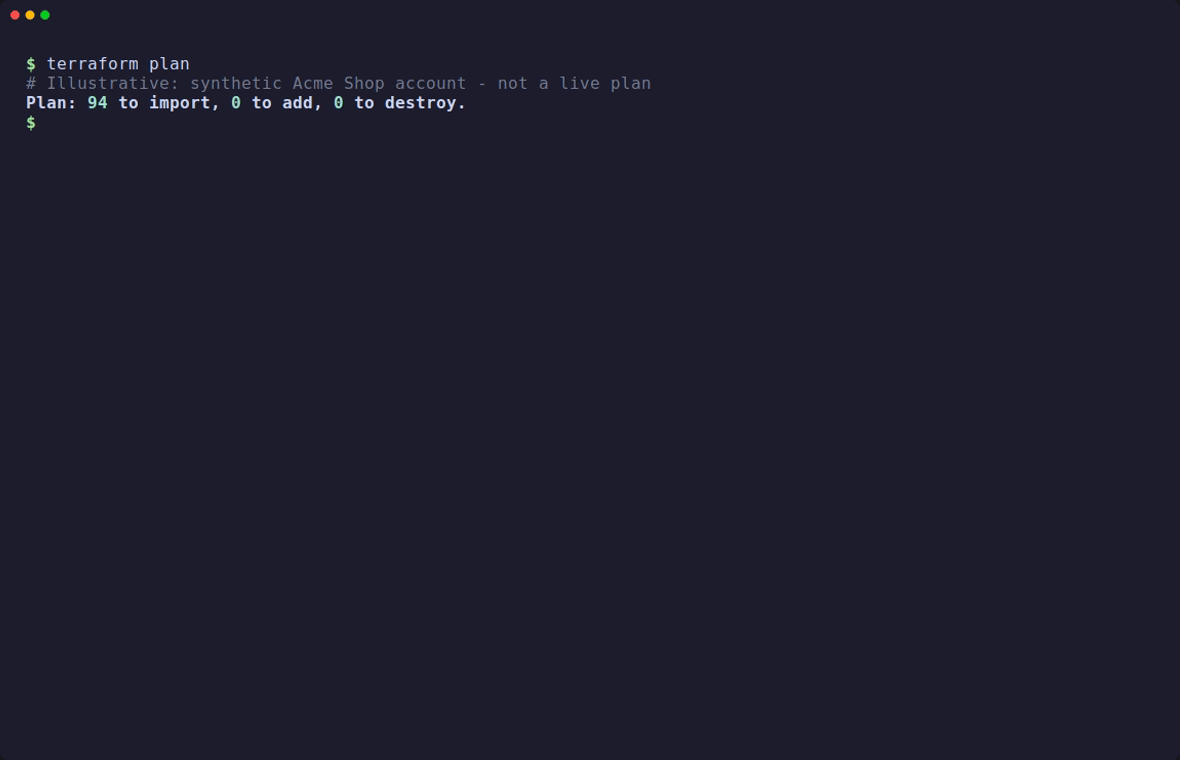
Everything below comes from “Acme Shop”, a fictional AWS account (123456789012, example.com) that contains no real infrastructure. The scanners and the codify pipeline are the real ones (RepliMap 0.6.0); nothing in the outputs is mocked. The scan found 122 resources, which became a graph of 106 nodes and 128 edges. 94 imports across 40 resource types were generated, and the Terraform passes terraform validate (1.14.5). 10 resources (7 types) are graph-only and not generated, 3 were skipped because CloudFormation owns them, and 15 were skipped because they are AWS defaults or service-owned.
The dependency graph
Interactive: drag, zoom and click nodes. It is a single self-contained HTML file with no external requests. Open full screen.
The generated Terraform
25 files, written to disk by replimap codify. Pick a file, or use the arrow keys in the list. Download all (.zip).
Where the graph becomes code: real cross-resource references in these files
- The HTTPS listener references its ACM certificate,
certificate_arn = aws_acm_certificate.origin_acmeshop_example_com.arn - A Route53 alias record references the load balancer,
zone_id = aws_lb.acme_shop_web.zone_id - The CloudFront origin points at the same load balancer,
domain_name = aws_lb.acme_shop_web.dns_name
Those lines are highlighted in the viewer. Then see : one import block per resource, so Terraform adopts what already exists instead of recreating it.
alb.tf
Raw file# Generated by RepliMap Codify resource "aws_lb" "acme_shop_web" { drop_invalid_header_fields = false enable_deletion_protection = true idle_timeout = "60" load_balancer_type = "application" name = "acme-shop-web" security_groups = [aws_security_group.acme-shop-alb.id] subnets = ["subnet-3bb0afd570fce1aef", "subnet-33c61b056a67b03e2"] tags = { CostCenter = "cc-1042" Environment = "prod" Name = "acme-shop-web" Owner = "platform-team" Project = "acme-shop" }} resource "aws_lb_listener" "acme_shop_web_http_80" { default_action { order = 1 redirect { port = "443" protocol = "HTTPS" status_code = "HTTP_301" } type = "redirect" } load_balancer_arn = aws_lb.acme_shop_web.arn port = 80 protocol = "HTTP" tags = { CostCenter = "cc-1042" Environment = "prod" Name = "5c1e9a7b3d2f4e60" Owner = "platform-team" Project = "acme-shop" }} resource "aws_lb_listener" "acme_shop_web_https_443" { certificate_arn = aws_acm_certificate.origin_acmeshop_example_com.arn default_action { order = 1 target_group_arn = aws_lb_target_group.acme-shop-web-ecs.arn type = "forward" } load_balancer_arn = aws_lb.acme_shop_web.arn port = 443 protocol = "HTTPS" tags = { CostCenter = "cc-1042" Environment = "prod" Name = "5c1e9a7b3d2f4e60" Owner = "platform-team" Project = "acme-shop" }} resource "aws_lb_target_group" "acme-shop-web-ec2" { deregistration_delay = "30" health_check { enabled = true healthy_threshold = 3 interval = 30 matcher = "200" path = "/healthz" port = "traffic-port" protocol = "HTTP" timeout = 5 unhealthy_threshold = 3 } load_balancing_algorithm_type = "round_robin" name = "acme-shop-web-ec2" port = 8080 protocol = "HTTP" tags = { CostCenter = "cc-1042" Environment = "prod" Name = "acme-shop-web-ec2" Owner = "platform-team" Project = "acme-shop" } target_type = "instance" vpc_id = aws_vpc.acme-shop-prod.id} resource "aws_lb_target_group" "acme-shop-web-ecs" { deregistration_delay = "30" health_check { enabled = true healthy_threshold = 3 interval = 30 matcher = "200" path = "/healthz" port = "traffic-port" protocol = "HTTP" timeout = 5 unhealthy_threshold = 3 } load_balancing_algorithm_type = "round_robin" name = "acme-shop-web-ecs" port = 8080 protocol = "HTTP" tags = { CostCenter = "cc-1042" Environment = "prod" Name = "acme-shop-web-ecs" Owner = "platform-team" Project = "acme-shop" } target_type = "ip" vpc_id = aws_vpc.acme-shop-prod.id}What you don't see
- Lambda functions, ECS services and task definitions, API Gateway resources and SSM parameters appear in the graph but are not generated as Terraform.
- EC2
user_datais never stored, and secret values are never read. - Resources owned by CloudFormation and AWS-default resources are skipped on purpose.
More on what RepliMap reads and sends on the What RepliMap talks to page.
40 seconds in the terminal
The terminal output replays the synthetic account's numbers. The terraform plan line is illustrative.
Run it on your own account
Read-only, local, and nothing is uploaded.
pip install replimapThen follow the quick start or read the docs.